Password Entropy Explained: What Actually Makes a Password Strong
Password advice often boils down to vague rules — "use symbols," "make it longer," "don't reuse passwords" — without explaining what actually makes one password harder to crack than another. The real answer comes down to a concept called entropy, which measures password strength in a way that can be calculated, not just guessed at.
What password entropy actually measures
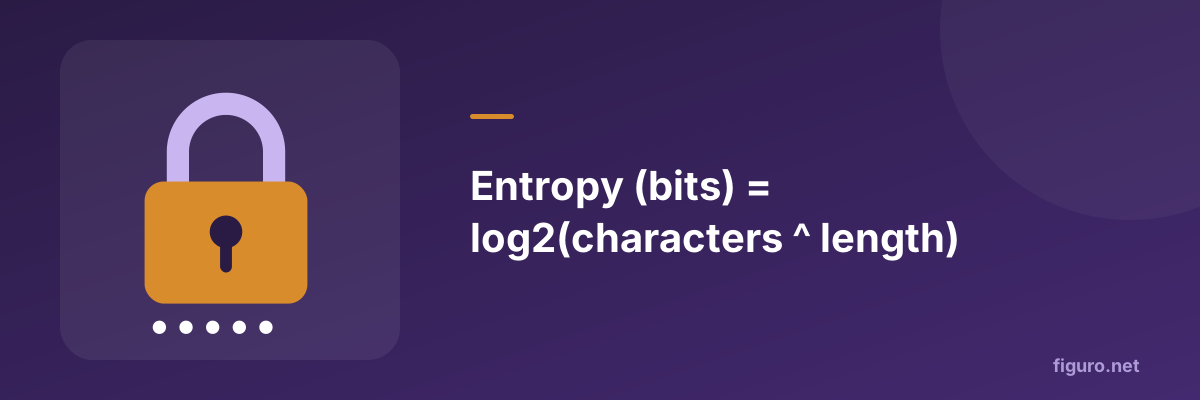
Entropy measures how many possible combinations an attacker would have to try before being guaranteed to find your password, expressed in bits. Each additional bit of entropy doubles the number of guesses required — so entropy grows exponentially, not linearly, which is why small changes to password length or character variety can make an enormous practical difference.
The "possible characters" figure depends on which character sets are used: roughly 26 for lowercase letters alone, 52 for upper+lowercase, 62 adding digits, and around 94 once common symbols are included.
Why length matters more than complexity
This formula reveals something counterintuitive: adding length usually increases entropy more than adding character variety. An 8-character password using all 94 available characters has about 52.4 bits of entropy. A 16-character password using just lowercase letters (26 characters) has about 75.2 bits — despite using a far smaller character set, the extra length makes it dramatically harder to crack. This is the reasoning behind the modern shift toward encouraging long passphrases over short, symbol-heavy passwords that are hard to remember and often only marginally more secure.
The origin of entropy
The idea of entropy as a measure of information comes from Claude Shannon, whose 1948 paper A Mathematical Theory of Communication founded information theory. Shannon measured uncertainty in bits, where each bit halves the number of possibilities. Applied to passwords, it tells you how many guesses an attacker might need. A password with N bits of entropy has 2^N possible values if it was chosen randomly, so each additional bit doubles the search space.
How to calculate it
For a random password, entropy equals length × log2(size of character set). For example:
- 8 random characters from a set of 94 printable symbols: about 52.4 bits.
- 12 random characters from the same set: about 78.7 bits.
- 16 random lowercase letters: about 75.2 bits.
- 4 random words from a 7,776-word Diceware list: about 51.7 bits.
- 6 random words from the same list: about 77.5 bits.
These figures only apply when each character or word is truly chosen at random. A password people invent, such as a pet's name followed by a year and an exclamation point, has far less entropy than the formula suggests, because attackers try common patterns first.
Passphrases and the history of advice
In 1995 Arnold Reinhold introduced Diceware, a method of generating passphrases by rolling dice to pick words from a numbered list. In 2011 the webcomic xkcd illustrated the same idea with the phrase "correct horse battery staple," showing that a few random common words can be both stronger and easier to remember than a short complex password. Earlier guidance recommended forced symbols and regular password changes. Bill Burr, the author of a 2003 US government document that recommended these rules, later said he regretted much of the advice. Modern guidelines from NIST, updated in 2017, favor length, blocklists of known breached passwords and no mandatory rotation unless there is evidence of a compromise.
What actually protects you
- Use a different password for every account, so one breach does not expose others.
- Use a password manager to generate and store long random passwords.
- Turn on two-factor authentication, preferably with an authenticator app or a hardware key.
- Check whether your email appears in known breaches using a reputable service.
Entropy is also not the whole story, because a strong password does not help if a website stores it carelessly or if you are tricked into typing it on a fake page. The Password Generator on this site creates random passwords in your browser, and the generated password is never sent anywhere.
Want a strong, random password generated automatically to your exact specifications?
Try the Calculator →What actually makes a password weak, regardless of entropy math
Entropy calculations assume an attacker is guessing randomly across the full possible character space — but real-world password cracking rarely works that way. Dictionary attacks, common substitution patterns (like "P@ssw0rd"), and reused passwords from data breaches let attackers skip most of that search space entirely. A password can have technically high entropy by the formula above and still be weak in practice if it's a recognizable word with predictable substitutions, because attackers try likely patterns first, not random combinations.
Practical takeaways for generating strong passwords
- Prioritize length. Aim for at least 12–16 characters where the service allows it — length has an outsized effect on entropy.
- Use a full random mix of uppercase, lowercase, numbers, and symbols when a password needs to be short, since character variety matters more at shorter lengths.
- Avoid predictable patterns — dictionary words, keyboard sequences (like "qwerty"), and common substitutions are the first things automated cracking tools check.
- Never reuse passwords across accounts. Even a mathematically strong password becomes worthless everywhere else once it leaks in a single data breach.
- Use a password manager so you don't need to remember long, random, unique passwords for every account — this removes the temptation to reuse or simplify passwords for memorability.
Put this guide into practice
Password Generator — Strong random passwords with custom options.